How IBM CIO Matt Lyteson uses Project Lightwell to protect his company's software supply chain

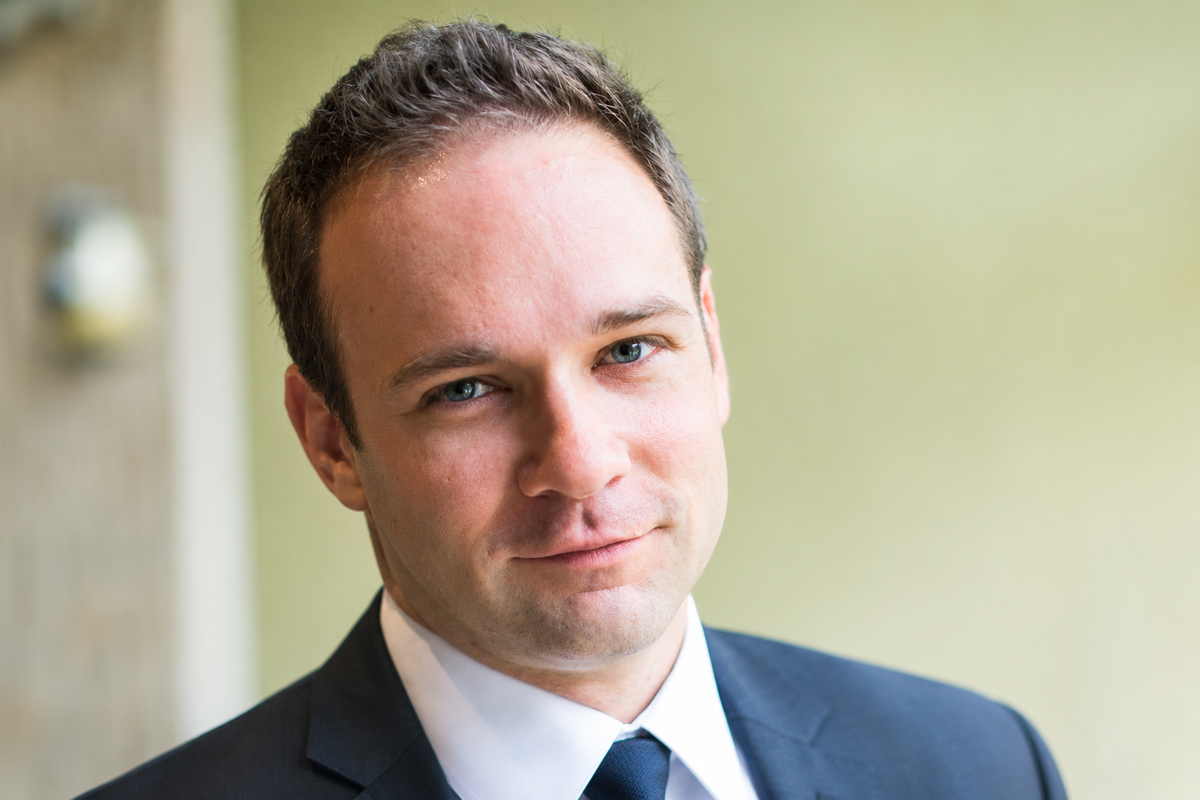
When IBM and Red Hat announced Project Lightwell earlier this year, a project designed to help companies safely update open source libraries, IBM CIO for technology platform transformation Matt Lyteson's team was one of the first to use and test the software on IBM's own pipeline.
But it's not just an IBM problem. As Lyteson pointed out, many companies run up to 90% of their software on top of open source libraries. The problem is exacerbated by the fact that updating these libraries can break software that works, software that is essential to running a business. As a result, companies often leave these libraries outdated and their software vulnerable, even as AI tools help attackers find security flaws faster than ever.
There's research to back up this concern. In a 2023 study of more than 18,000 Java software projects, researchers at the University of Auckland and Victoria University of Wellington found that 72% of the library dependencies were outdated. When they tested dependency updates, over 11% broke the underlying software to the point that it prevented it from compiling. That helps explain why companies might be reluctant to upgrade libraries, even when they know they should.
Abby Kearns, CEO at ActiveState, a firm that focuses on keeping the open source software supply chain safe, says Project Lightwell is proof the industry is finally taking this problem seriously.
"When institutions of that scale stand up coordinated programs around open source supply chain protection, the consensus has changed. This is no longer treated as a niche security topic. It is a crisis and recognition is finally catching up to the pace at which the exposure has been building," Kearns told me in a FastForward profile in June.
If you want a recent proof point, consider the PHP vulnerability that appeared in October, forcing many companies and governments to take their websites offline until they could install the patch. It's a clear case of just how serious these vulnerabilities can be to the health of the software ecosystem.
What is Lightwell
Lightwell solves the big problem of patching in place without requiring a full-scale upgrade of the underlying open source libraries, a process that requires a long testing cycle to ensure it doesn't break the underlying software.
"So rather than going through a whole upgrade cycle, I can now pull the patch from the Lightwell repository, that patched version of the library that my application is using and get that into production very very quickly," he said. "Then I can be assured it's fixed, it's non-breaking. I'm using the same version of the library as before. It's just the patched version of that."
Lightwell isn't free, however. IBM and Red Hat sell access to the patch repository through an annual subscription, with an additional premium offering for companies that want to request specific fixes. Pricing isn't publicly available, but likely doesn't come cheap. It's worth noting it offers free access to universities, NGOs and think tanks.
While that addresses the immediate vulnerability, it doesn't solve the modernization issue. The old library is still in place, and it would behoove companies to get with the latest versions as soon as they can. Lyteson says this doesn't replace application modernization efforts, although AI tools may help accelerate updating them.
"I don't have any of my team saying, 'Oh, I'm just going to rely on Lightwell for now,'" he said. "Myself, like many other CIOs in the industry, we have roadmaps for and disposition plans for every single one of our applications."
Lightwell in action
Lyteson's team was one of the first to test Lightwell in a real-world deployment. According to the company, within 24 hours of plugging Lightwell into the network, they were able to identify and patch 55 vulnerabilities across multiple Java applications.
He says the value becomes obvious pretty quickly. "The Lightwell network gives me access to a repository of these remediated libraries, and I just plug into that in my pipeline, and it's ready to go." While it's not comprehensive of course, it is growing fast, and as of when I spoke to him last month, he says it has grown to 40,000 patches.
Lyteson sees the urgency only increasing as AI makes it easier for bad actors to find and exploit vulnerabilities, forcing companies to get smarter about how they defend themselves. "I think a good analogy is like the lockpick just got a lot smarter, and so we as the locksmiths need to come in, and we need we need to get a lot smarter too," Lyteson said.
Funnily enough in the week prior to receiving Lightwell for testing, Lyteson discussed the need to be more vigilant about patching with his team. "Literally the week before we plugged into Lightwell, I was sitting down with some teams, looking at where we needed to address vulnerabilities and telling the teams, 'I need you to upgrade to a new version,'" he said. "And they were telling me, Matt, that's going to take a little bit of time. And then we plug in Lightwell, and that conversation entirely went away."
Lightwell certainly is a step in the right direction, helping teams update applications with certified patches without requiring a potentially disruptive software upgrade, but companies can't stop there. They must continue to have update plans running in parallel. Lightwell just gives them more flexibility, knowing a patch is in place.